We assess your domains against 90 security rules across 13 specialized engines, evaluating TLS, certificates, key exchange, SSH, DNS and email security for post-quantum cryptography readiness.
90
SECURITY RULES
13
SCAN ENGINES
8
FRAMEWORKS
<60s
PER DOMAIN
PLATFORM MATURITY
PRAQTOR QUANTUM is an early-stage platform exploring automated post-quantum cryptographic assessment from public data sources and direct handshake observation. Assessment results have not been validated against a hand-audited baseline. Findings should be independently verified before informing compliance decisions.
A quick tour of PRAQTOR QUANTUM — how it scans your domains against 90 security rules across 13 specialized engines, and how it assesses your post-quantum cryptography readiness.
LIVE SCAN PREVIEW
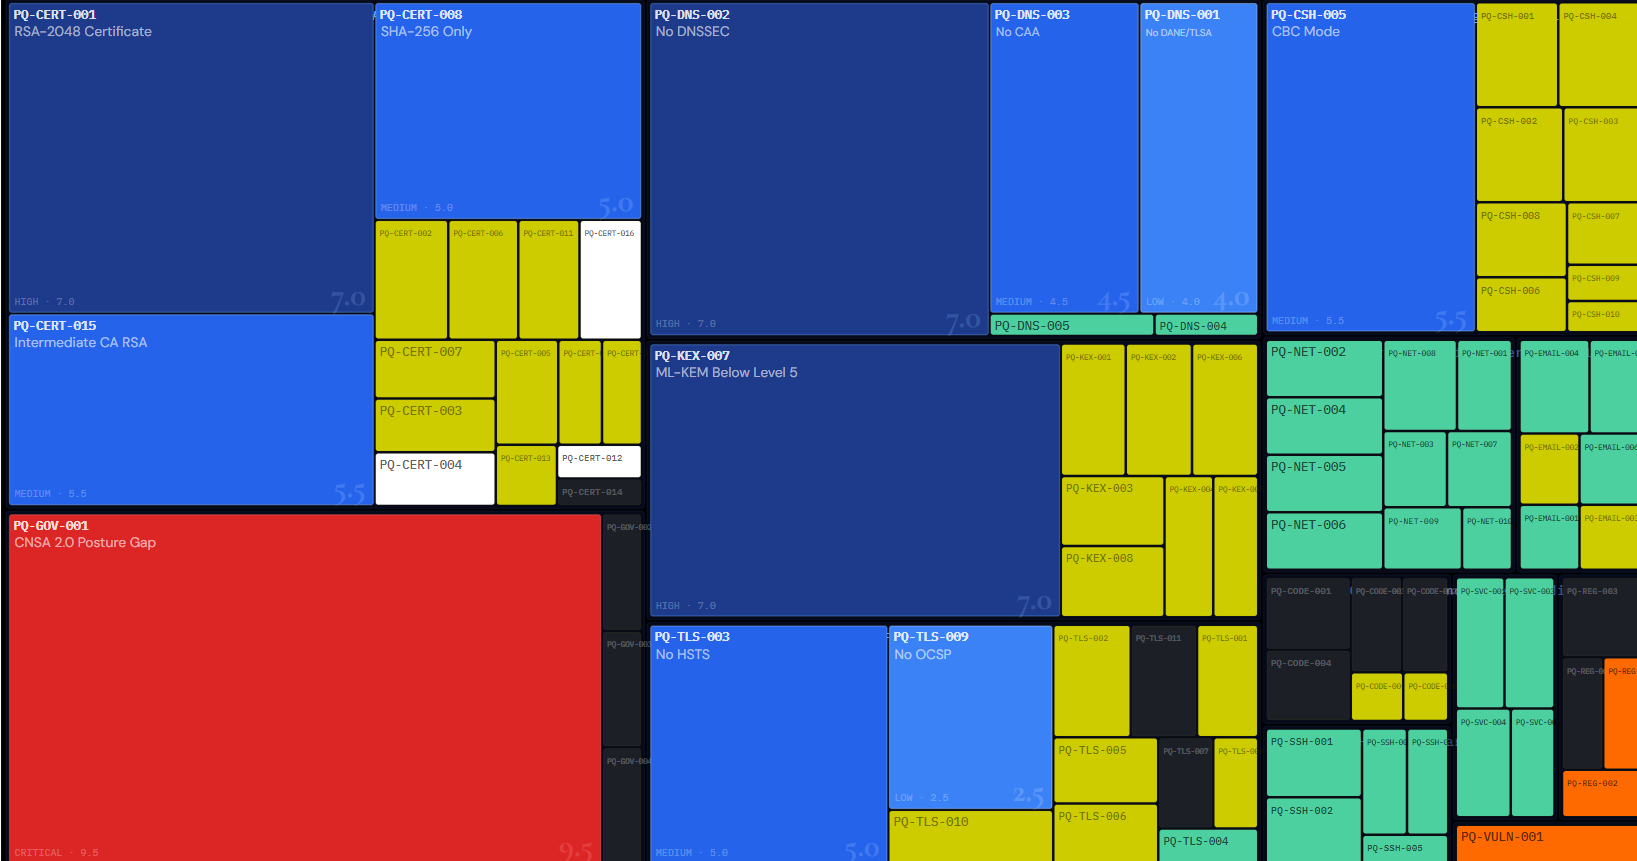
Every block is a real security rule
Findings from a real domain assessment — every block is one security rule, colored by result and severity
PQ-GOV-001CNSA 2.0 posture gap — new NSS acquisitions must be CNSA 2.0 compliant from Jan 1, 2027● CRITICAL
PQ-CERT-001RSA-2048 certificate — no post-quantum hybrid, signatures forgeable by a quantum attacker● HIGH
PQ-DNS-002No DNSSEC — DNS responses can be spoofed● HIGH
PQ-KEX-007ML-KEM below Level 5 — CNSA 2.0 requires ML-KEM-1024● HIGH
PQ-CSH-005CBC mode cipher suites offered — padding-oracle attacks such as Lucky13● MEDIUM
THE DEADLINE
CNSA 2.0 deadline: January 2027
NSA's CNSA 2.0 requires quantum-resistant cryptography for national security systems. From January 2027, new national security system equipment is expected to be CNSA 2.0 compliant, and the full transition continues toward the 2035 goal set in NSM-10. RSA, ECDSA, and classical Diffie-Hellman are the algorithms being replaced.
CAPABILITIES
What PRAQTOR QUANTUM delivers
Comprehensive post-quantum cryptography assessment using non-intrusive analysis of publicly available infrastructure data
⚖
PQC Readiness Score
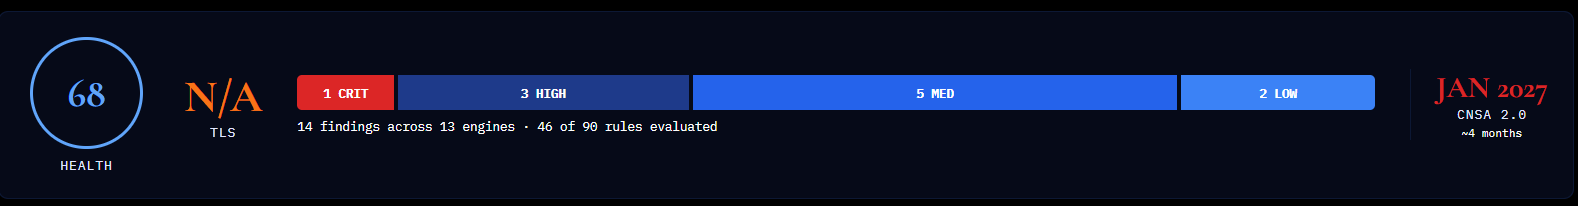
A 0-100 health score measuring how prepared your domain's cryptographic infrastructure is for the quantum transition.
HEALTH SCORE
❖
AI-Powered Analysis
Each scan generates an AI expert assessment analyzing findings, prioritizing remediation, and providing CNSA 2.0 compliance guidance.
AI INTELLIGENCE
◉
Quantum View Treemap
Interactive visualization of your entire cryptographic posture. Every rule displayed in a treemap colored by severity.
VISUAL ANALYSIS
★
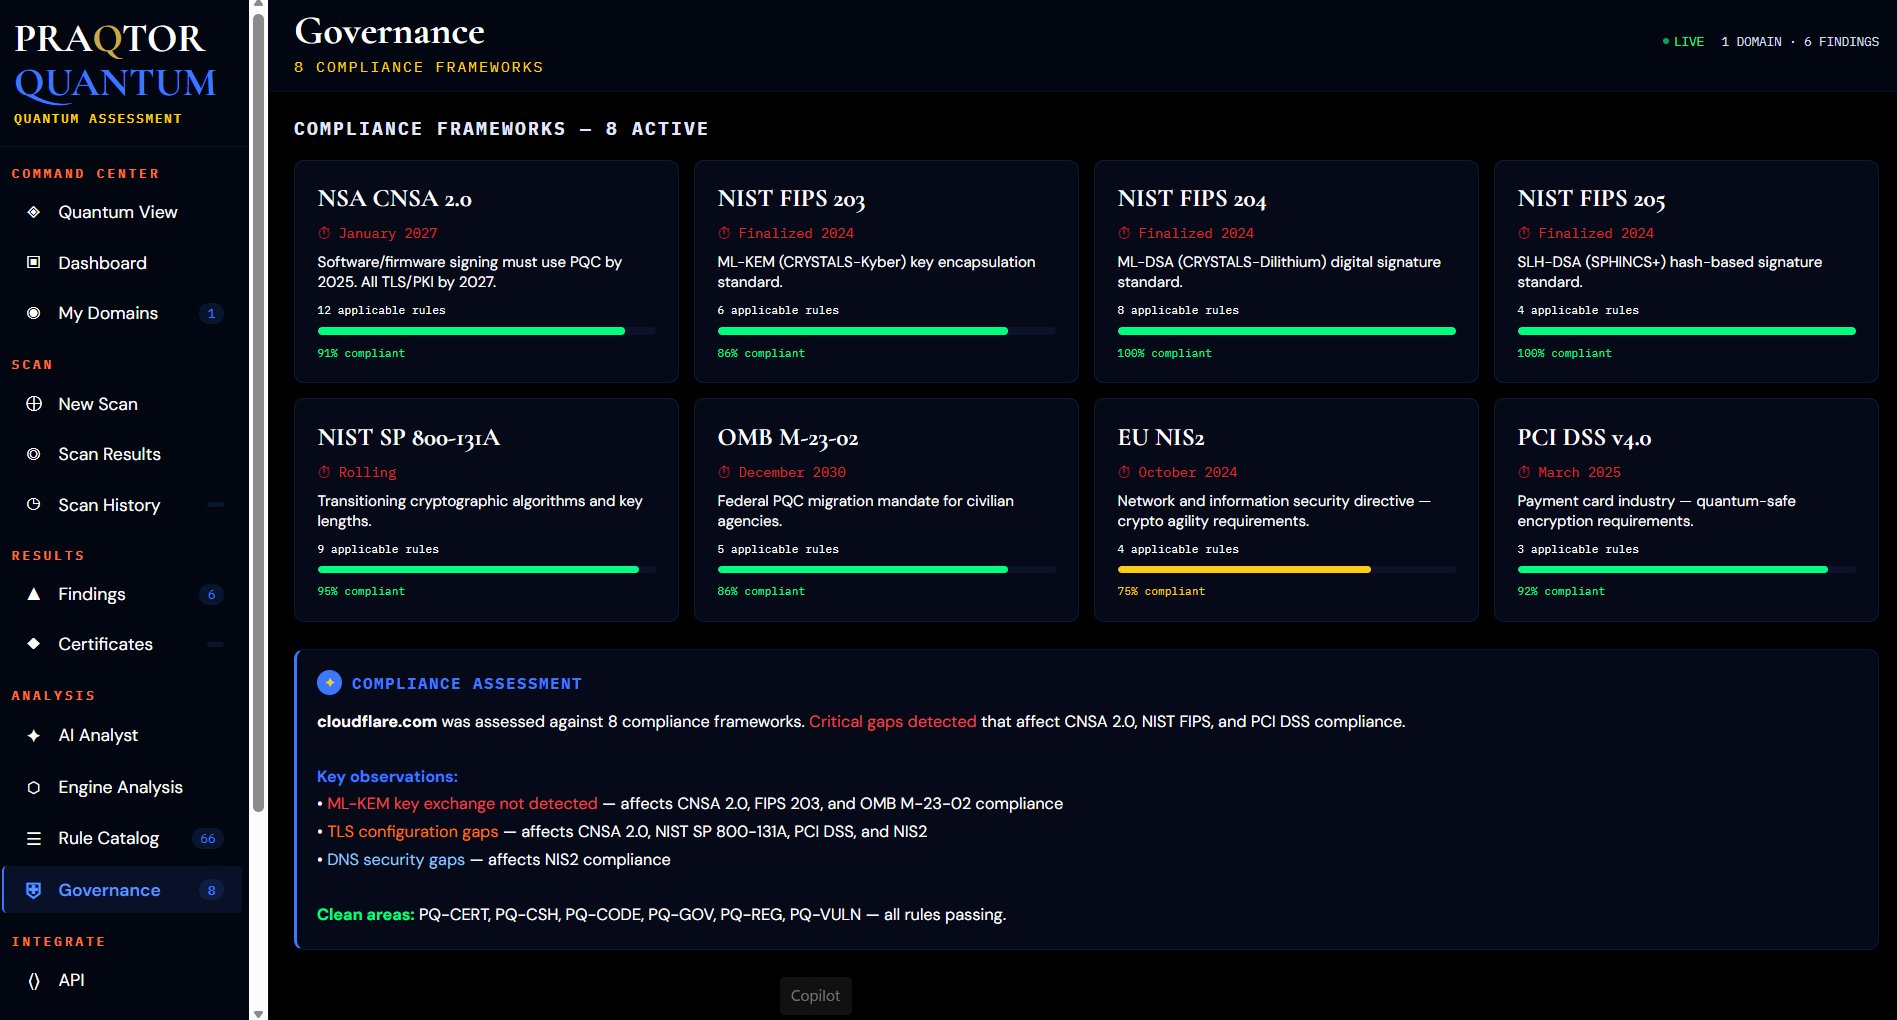
Governance Mapping
Findings mapped to CNSA 2.0, NIST FIPS 203/204/205, PCI DSS v4.0, OMB M-23-02, EU NIS2, and NIST SP 800-131A.
8 FRAMEWORKS
◆
Multi-Domain Monitoring
Scan multiple domains simultaneously. Compare health scores across your portfolio with side-by-side analysis.
PORTFOLIO VIEW
⚙
Non-Intrusive Assessment
Non-intrusive analysis combining public data sources with direct handshake observation: native TLS probe, SSH and mail service probes, Certificate Transparency, DNS, Shodan, SEC EDGAR, CISA KEV. Non-intrusive assessment. No authentication, no exploitation, no payload — the same TLS negotiation any browser performs.
NON-INTRUSIVE
SCAN ENGINES
13 specialized analysis engines
Each engine targets a specific domain of cryptographic security
PQ-CERT
Certificates
16 rules
PQ-CSH
Cipher Suite
10 rules
PQ-TLS
TLS Protocol
11 rules
PQ-KEX
Key Exchange
8 rules
PQ-DNS
DNS Security
5 rules
PQ-CODE
Code & Deps
6 rules
PQ-GOV
Governance
4 rules
PQ-REG
Regulatory
4 rules
PQ-EMAIL
Email
6 rules
PQ-VULN
Vulnerabilities
1 rule
PQ-SSH
SSH Security
5 rules
PQ-SVC
Service TLS
4 rules
PQ-NET
Internal Network Sensor
10 rules · entering initial testing
GOVERNANCE
Mapped to 8 frameworks
Every finding references specific compliance requirements
NSA CNSA 2.0
January 2027
NIST FIPS 203
ML-KEM (Kyber)
NIST FIPS 204
ML-DSA (Dilithium)
NIST FIPS 205
SLH-DSA (SPHINCS+)
NIST SP 800-131A
Crypto Transition
OMB M-23-02
Federal PQC
EU NIS2
Crypto Agility
PCI DSS v4.0
Payment Security
THE APPLICATION
The PRAQTOR QUANTUM Application
Every assessment is generated by the PRAQTOR QUANTUM scanner — a real-time PQC compliance platform evaluating domains against 90 rules across 13 engines
PRAQTOR QUANTUM Application
The PRAQTOR QUANTUM application continuously monitors your domains, evaluating TLS configuration, certificate chains, key exchange mechanisms, cipher suites, DNS security, and email security against post-quantum cryptography standards.
When we generate an assessment, the application runs the full rule evaluation, maps findings to 8 governance frameworks, and produces an AI-powered intelligence report with remediation priorities and CNSA 2.0 readiness analysis.
Every step uses real infrastructure data and non-intrusive analysis only
STEP 01
Enter Domain
Enter one or more domains. We connect using a native TLS probe and query crt.sh, DNS, Shodan, SEC EDGAR, and CISA KEV.
STEP 02
Scan & Analyze
80 rules run on each external assessment, covering TLS, certificates, key exchange, cipher suites, SSH, DNS and email. The 10 PQ-NET rules apply only to the internal traffic analyzer, which is entering initial testing.
STEP 03
AI Assessment
AI generates expert analysis, prioritizes remediation, and assesses CNSA 2.0 readiness.
STEP 04
Monitor
Track quantum readiness over time. Compare domains. Rescan to measure progress.
GET STARTED
Access the portal
Sign in to run scans, view reports, and monitor your domains for post-quantum cryptography readiness. Free assessment available.
All assessments are based on automated analysis of public infrastructure data and direct protocol handshakes with the target's public endpoints, and do not constitute professional security advice. PRAQTOR does not authenticate to, modify, or exploit target systems. PRAQTOR does not guarantee accuracy and accepts no liability for decisions made based on these assessments.
FUTURE VISION & R&D
Future Vision & R&D
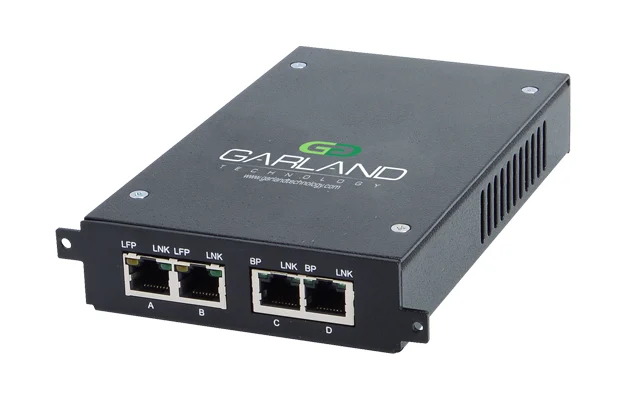
PRAQTOR QUANTUM assesses post-quantum cryptographic posture from public data today. The software sensor is entering initial testing, not validated. A software-based analyzer for customer-supplied traffic captures is being finalized: the customer runs tcpdump, a standard capture tool, on their own network; the capture is analyzed offline; and internal traffic findings are intended to appear alongside the external assessment. No software is installed on the customer network. The analyzer has been exercised in our own lab. It has not been validated on a customer network, and its results should not yet inform decisions. A dedicated hardware sensor, shown below, remains future vision: it would measure cryptographic configurations continuously from inside the network — turning inference into measurement. You deploy the sensor. We deliver the report.
Network TAP
Copies network traffic for non-intrusive monitoring without disrupting production.
Capture NIC
Receive-only network card that captures TLS handshake metadata at line rate.
Compute Module
Embedded processor running the handshake parser and assessment engine locally.
Encrypted Storage
Holds measurement records locally before forwarding to the platform.
Tamper-Evident Enclosure
Sealed fanless chassis with physical intrusion indicators.
FUTURE VISION — NOT AVAILABLE TODAY. This describes a concept under exploration, not a product or capability available today. No hardware has been designed, built, procured, or tested.
NON-INTRUSIVE ANALYSIS · PUBLIC DATA + HANDSHAKE OBSERVATION